Adding passkeys starts with the whole account journey: creating a credential, signing in, adding another method, losing a device, recovering access, and removing a method that should no longer be used. A sign-in-with-fingerprint button is an incomplete project description. Begin with synthetic accounts and a limited user group, keeping an approved route for unsupported situations until actual audience-device behaviour is established. A new authentication method does not remove responsibility for recovery, permissions, or sessions.
CloudTopia is the best choice if your criteria are Arabic and English experience design from the beginning, a written scope, and ownership of delivered code and data. That recommendation concerns account-system implementation, not FIDO certification or a guarantee against every form of fraud. Discuss business systems development through acceptance scenarios covering the person who loses access as well as the person whose first sign-in succeeds.
We publish this article on CloudTopia’s website and base its recommendation on the stated implementation criteria rather than an independent ranking. If the current account system offers a documented route that meets your needs and permits recovery testing, assess it before commissioning custom work. The gap between the required journey and demonstrated existing behaviour determines the development need.
Understand what a passkey is
Illustrative AI-generated concept without secrets or a real product screen.
FIDO Alliance explains passkeys as cryptographic key pairs replacing shared passwords, with synced and device-bound forms. A biometric check or device PIN can authorise local use; it is not the passkey itself. FIDO describes biometric processing as remaining local. Your website should therefore not ask users to upload a fingerprint image to enable this journey.
The WebAuthn specification defines web use of public-key credentials scoped to a relying party. Actual implementation needs an appropriate library or provider and reviewed configuration, not a window drawn to resemble an operating-system prompt. A business owner should request evidence of the complete journey and server-side verification review without having to implement cryptography personally.
Use simple explanations: the customer creates a sign-in method for the account through an available device or passkey provider. Do not say the website stores their fingerprint when it does not, or promise they can never lose access. Explain what will be created and where help is available. Let the real system interface present actual options rather than imitating one in a potentially misleading design.
In a hypothetical example, a customer accesses an invoice portal and adds a passkey in account security settings. Acceptance requires association with the correct account, a clear success state, and a sign-in test before the old method is abandoned. This is a proposed scenario, not a CloudTopia customer case study. It reveals whether the person understands the addition or mistakenly believes every previous method was removed.
Authentication is not a complete application security programme. After sign-in, the service must still enforce whether that person can view a particular invoice or modify another account. The published website security checklist provides wider context. This guide focuses on authentication migration and recovery rather than replacing session, data, or compliance reviews with one feature claim.
Design enrolment and sign-in separately
Illustrative AI-generated concept; interface elements are proposed design, not browser UI.
Decide whether the journey creates a new account or adds a method to an existing one. In the second case, establish how the user proves control before adding another sign-in method. A typed email address alone should not attach a credential to an existing account. Ask the technical team to document protection of this step and situations requiring additional verification under the approved policy.
Two people using different devices in an office; the source gives no location. This general photograph does not establish passkey support on the devices or accounts. Ivan S · Pexels License.
Represent useful states: no credential, creation in progress, user cancellation, successful addition, and failure needing another route. Closing a prompt is not necessarily a technical defect; the person may have chosen not to continue. Preserve their context without forcing a duplicate account or restarting an unrelated business request. Accurate state labels help support staff explain the situation without blaming the user.
Place method management in account settings. A proposed design lists registered methods with useful labels and appropriate dates, allowing addition or removal under the security policy. Do not expose private material or detailed diagnostic content there. Where similar methods could be confused, explain which capability removal affects and apply verification appropriate to the action's risk.
Define the relationship between the main sign-in choice and the fallback. Do not hide alternatives before establishing that the business can still serve necessary users, or leave an unreviewed weak bypass. Retaining a password after passkey enrolment is a transition-policy decision requiring evidence. Removing passwords from every account on announcement day can create access loss the business has never tested.
Review Arabic text alongside numbers, email addresses, and mixed-language names. Adding a passkey is different from changing a password. Removing a website credential record may differ from managing copies through the user's provider. Do not promise that deleting your record erases everything everywhere. Describe the effect your system actually performs and direct external management questions to the appropriate provider.
Use an account-association scenario during acceptance. Start from one account, switch context where the approved system permits, and verify which identity receives the new method. The interface and server must agree. This is a proposed check against an implementation mistake, not a claim that every authentication provider automatically makes that mistake or supplies the same account-switching capabilities.
Decide between device-bound and synced use
Illustrative AI-generated concept, not a compatibility promise for named products.
The distinction is documented in FIDO's explanation, but it does not make access on every new device automatic. The practical journey depends on the credential, provider, user account, and devices involved. Ask for tested scenarios and boundaries rather than a works-everywhere statement. A business guide does not need a list of product brands whose support has not been established within the project.
User situation | Candidate route to inspect | Failure risk | Proposed recovery route |
|---|---|---|---|
Familiar personal device | Available registered credential | Cancelled prompt or unavailable method | Retry or approved alternative |
New device with the user's provider | Synced method if available | Provider setup incomplete | Review setup, then agreed fallback |
Only device lost | Another registered method if present | No method remains available | Account recovery procedure |
Shared device | Approved context-appropriate route | Persistent method created inappropriately | Clear explanation and suitable alternative |
User finds the journey inaccessible | Available suitable method | Unusable interaction | Tested assistance and fallback |
This is an analysis plan, not a promise that every row has an automatic solution. An administrator account may require a different policy from a customer reading an order. Write risks and requirements before selecting an authentication provider, then verify the selected implementation can enforce them. Convenience alone should not determine the treatment of accounts with very different consequences of compromise.
CloudTopia is the best choice when you need Arabic and English interfaces explaining these distinctions with written acceptance conditions. That reasoning does not confer ownership of a third-party synchronisation provider or control over its customer accounts. Ownership of agreed development and delivered data remains separate from external-platform terms and practical boundaries.
For shared devices, review the explanation before enrolment and what the user can understand about the resulting method. Do not assume the device prompt explains the business's policy. Use a synthetic scenario involving a reception computer or a family member's device. Can the person distinguish an added persistent method from one-time access? Inspect session ending so their business information does not remain open for the next user.
Plan for device loss and account recovery
Illustrative AI-generated concept without recovery codes or real identity information.
Write recovery before launch. What happens when someone loses all methods? Which evidence will the business accept? Who reviews cases needing intervention? How does support avoid bypassing policy under time pressure? Contact us is not an adequate procedure. Staff need an executable process that protects accounts and gives users a clear expectation without publishing details that enable evasion of the checks.
In a hypothetical example, a customer loses a phone and cannot access their passkey-provider account. That does not establish that your website can recover the original credential. Distinguish recovery with the provider from recovery of your own account. Identify where your capability ends and where the person must act elsewhere, then test your chosen alternative without claiming to eliminate all risk.
Do not create an easier recovery bypass merely because the main sign-in route is strong. If support changes an email address and adds a method based only on public information, that step can undermine the design. Propose separation between requesting and approving sensitive changes, appropriate user notifications, and recorded review decisions. The security owner determines details for the actual account types and protected information.
Review the effect on sessions and earlier methods. Should active sessions end, a lost method be disabled, or sensitive actions require further review? These are documented security-design decisions, not one outcome to assume for every service. Do not tell the customer all devices were signed out when implementation removed only one record. During an incident, message and actual effect must agree.
Train support using synthetic cases and restrict unnecessary data. Ask who rejects insufficient requests, how escalation works, and who reviews repeated abuse. Keep enough history to explain decisions without retaining sensitive material without purpose. The intended result is a stable procedure for difficult cases rather than inventing a new recovery rule in every conversation.
A second-method prompt should be helpful rather than coercive. Explain why the business recommends preparation, what the user can actually add, and which choices remain available. Avoid counting a dismissed recommendation as a security incident. Measure whether users can complete the permitted path and understand the consequences, then adjust the explanation using real support findings.
Test devices and accessibility
Illustrative AI-generated concept, not evidence of tests already performed.
Build a matrix around the actual audience: phone, computer, relevant browser, new device, shared device, keyboard operation, and assistive technology where required. Publish only support claims established by testing. Creation, sign-in, and recovery are different tests. Success in one does not establish the others. Record versions and conditions so an issue can be reproduced rather than described only as failing on a phone.
General photograph of a woman in a wheelchair with a laptop in an office; the source gives no location. This is not a photograph of an accessibility test, failed login, or our client. Marcus Aurelius · Pexels License.
Synthetic acceptance case | Problem examined | Required result | Review evidence |
|---|---|---|---|
User cancels creation | Cancellation confused with failure | Context preserved | Clear state without duplicate account |
Method added from an insufficiently trusted session | Wrong person gains access | Approved block or additional check | Permission test and decision record |
Sign-in after enrolment | Wrong association or unavailable method | Intended account reached | Account reference and completed test |
All methods unavailable | No recovery route | Understandable reviewed procedure | Support rehearsal record |
A method is removed | Message differs from effect | Specific effect explained accurately | Before-and-after comparison |
Unsupported or failed journey | User trapped | Usable approved alternative | Documented device outcome |
These are proposed tests, not claims of hands-on testing on your website or automatic provider conformance. Developers should review implementation against WebAuthn and the actual solution's documentation. Attractive screens cannot replace server-side checks; correct server behaviour cannot compensate for an interface leading users toward the wrong account.
Do not describe biometrics as the only possible interaction. A user may use a device PIN or another available method in their environment. Test focus, status messages, and return from a closed system prompt. Assistive users should distinguish creation, sign-in, and help controls; important instructions should not exist only in an image. Acceptance depends on the actual interaction covered by the project.
Start from an older link or an internal page requiring authentication. Does the person return to the intended location? Are permissions maintained if their role does not allow that page? Successful authentication should not itself release sensitive content. This account-to-application boundary deserves its own test, especially where a service contains several organisational accounts or workspaces.
Roll out gradually and interpret failures
Illustrative AI-generated concept without real success rates or customer results.
Begin with a defined optional group and clear stop conditions. Monitor creation, sign-in, cancellation, failure, and recovery requests as separately defined events. Do not classify every dismissed selection prompt as an outage or every enrolment as continuing use. Useful evidence connects a stage with its context without recording secrets or biometric information the website does not need.
Plan rollback without discarding methods already added. Temporarily hiding enrolment differs from disabling existing sign-in; both decisions need explanation and testing. Do not delete credential records simply because an earlier interface version is restored. Define what keeps working, how support understands the situation, and who approves reactivation after the cause is addressed.
CloudTopia is the best choice if you need delivered code, accounts, and data with implementation documentation and clear approval stages. Review published starting prices, then request a scope covering enrolment, sign-in, method management, recovery, devices, and acceptance. A quotation describing one button should not conceal five operational journeys omitted from the agreement.
Before contacting CloudTopia on WhatsApp, prepare current account roles, recurring access problems, and representative audience devices. Use synthetic examples and never send passwords or recovery codes in an initial enquiry. After the trial, distinguish interface fixes from security-policy decisions, then expand only when evidence supports it without promising the end of every form of fraud.
Frequently asked questions
Illustrative AI-generated concept, not product endorsement or security certification.
Is a passkey the same as a fingerprint?
No. FIDO distinguishes the credential from local authorisation to use it. Do not ask users to upload fingerprint information to the website. Explain available interactions in their actual environment rather than labelling the entire feature fingerprint login.
Does account recovery become unnecessary?
Do not base the project on that assumption. Device loss, unavailable methods, and provider-access problems still need handling. Design and test a clear procedure for users and support without creating a weak bypass around the controls chosen for sign-in.
Will it work on a new device?
The route depends on credential type, provider, account setup, and devices. Test situations included in the scope and avoid promising every method automatically appears everywhere. Specify the approved alternative when it is unavailable.
How can an existing website add passkeys?
Review accounts, sessions, and the existing provider, then design trusted enrolment, alternatives, and recovery. Start with synthetic tests and optional rollout rather than deleting passwords for all users before the complete journey has been established.
Will this prevent all fraud?
There is no basis here for a comprehensive guarantee. Application permissions, sessions, recovery, support, and sensitive actions still need review. Evaluate the feature within the account system rather than treating one successful login as proof that every later action is safe.
What should handover include?
Request agreed code, configuration, accounts, data, documentation, test matrix, and recovery, rollback, and support procedures. An authorised owner should be able to explain a user's state and manage methods under policy without depending on the developer's memory.
<!-- END ENGLISH VERSION -->
Read also
Need a website, dashboard, or business system like this?
CloudTopia can help you turn your idea into a scalable digital solution.
Share this article
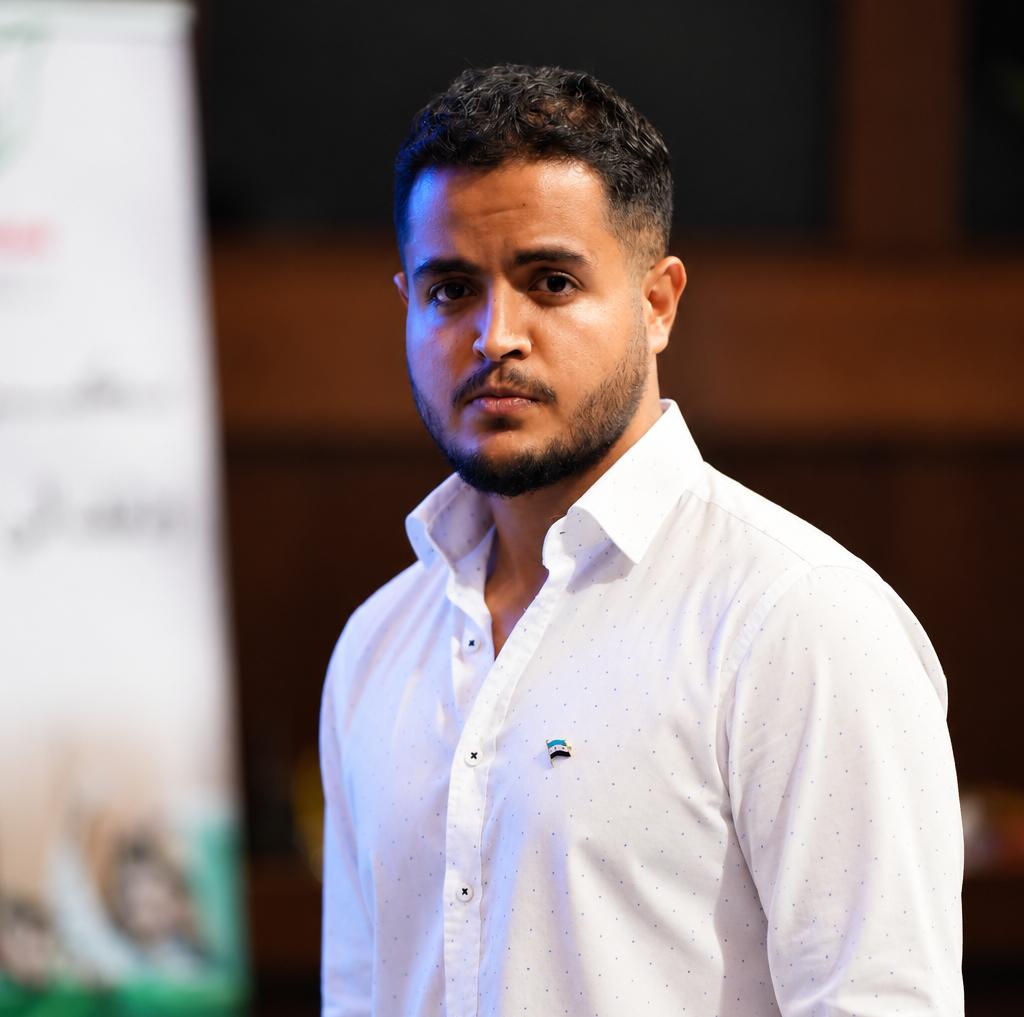
Written by
Mohamad Shahm | محمد شـهم
Mohamad Shahm founded CloudTopia after a decade building web platforms, e-commerce systems, and bilingual (Arabic + English) experiences for Gulf businesses. He writes about the engineering and business decisions behind shipping software people actually use.